Loading SOVA...
Loading SOVA...
The complete workflow — from scanning your project with SOVA to receiving a full CycloneDX SBOM with vulnerability analysis, license compliance, and dependency graph visualization.
Run SOVA on your project to extract dependency data from manifests and lock files.
sova scan --path .Upload the generated sova-manifest.json to SecureNexus via the web interface or API.
→ securenexus.ai/generateDownload a CycloneDX SBOM enriched with vulnerabilities, licenses, and metadata.
↓ sbom-cyclonedx.jsonRun SOVA against your project directory. It will detect all manifest and lock files, parse dependencies across all detected languages, detect security signals, and output everything to a single JSON file.
$ sova scan --path /path/to/your/project
For the best SBOM quality, use these recommended flags:
$ sova scan --path . --include-dev --strip-paths --output sova-manifest.json
--include-devInclude devDependencies for a complete inventory — SBOM should cover the full build surface.
--strip-pathsReplaces absolute paths with . in the manifest, avoiding leaking directory structure.
--outputExplicitly name the output file for clarity in CI/CD pipelines.
After the scan, SOVA prints a summary and writes sova-manifest.json:
Before uploading, you can inspect the manifest to verify what was captured. The file contains only dependency metadata — never source code, secrets, or environment variables.
{
  "version": "1.0",
  "tool": { "name": "@securenexus/sova", "version": "1.0.0" },
  "project": { "name": "my-app", "version": "2.1.0", "path": "." },
  "scan": {
    "languagesDetected": ["javascript", "python", "rust"],
    "totalFiles": 5,
    "totalDependencies": 313,
    "hasLockFiles": true
  },
  "applications": {
    "javascript": ["express_:_4.18.2", "lodash_:_4.17.21", ...],
    "python": ["requests_:_2.31.0", "boto3_:_1.28.0", ...],
    "rust": ["serde_:_1.0.197", "tokio_:_1.36.0", ...]
  },
  "dependencyGraph": { ... },
  "securitySignals": { "totalSignals": 0, "critical": 0, ... }
}Upload your manifest to SecureNexus to generate a full SBOM. There are two ways to do this:
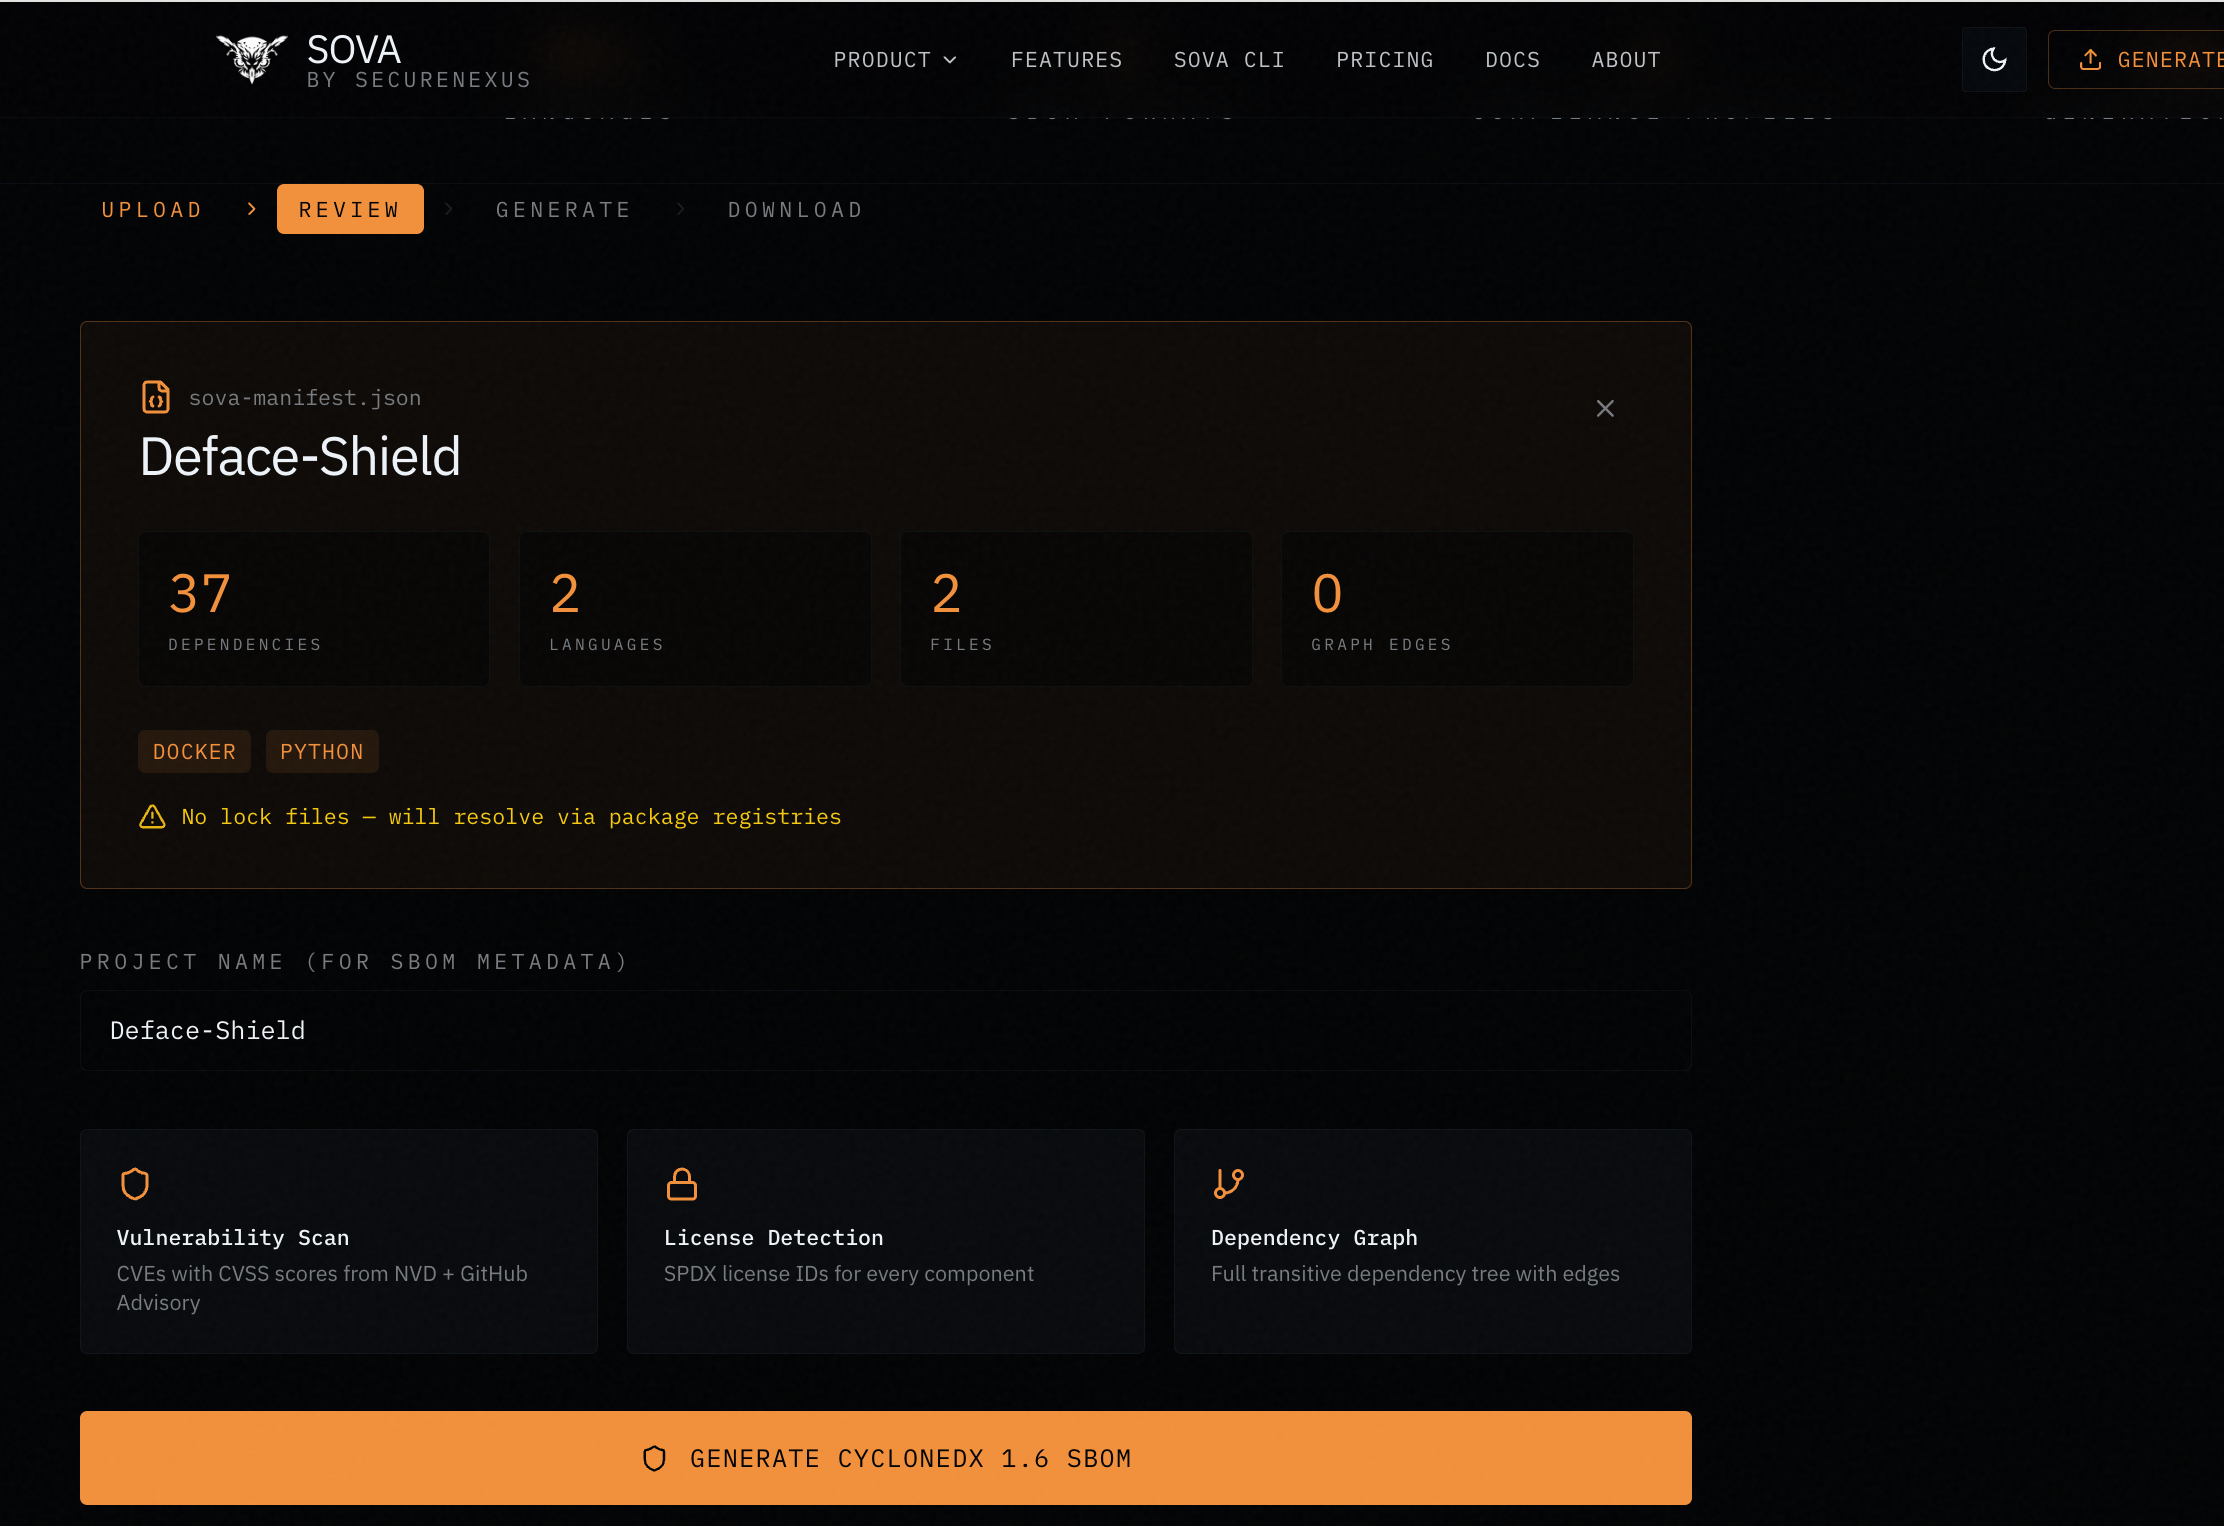
Go to securenexus.ai/generate and drag-and-drop your sova-manifest.json file. The web interface will:
For air-gapped or restricted environments where the machine running SOVA has no internet access:
Safe to transfer: The manifest contains only package names, versions, and dependency relationships. No source code or secrets are ever included, making it safe to transfer across network boundaries.
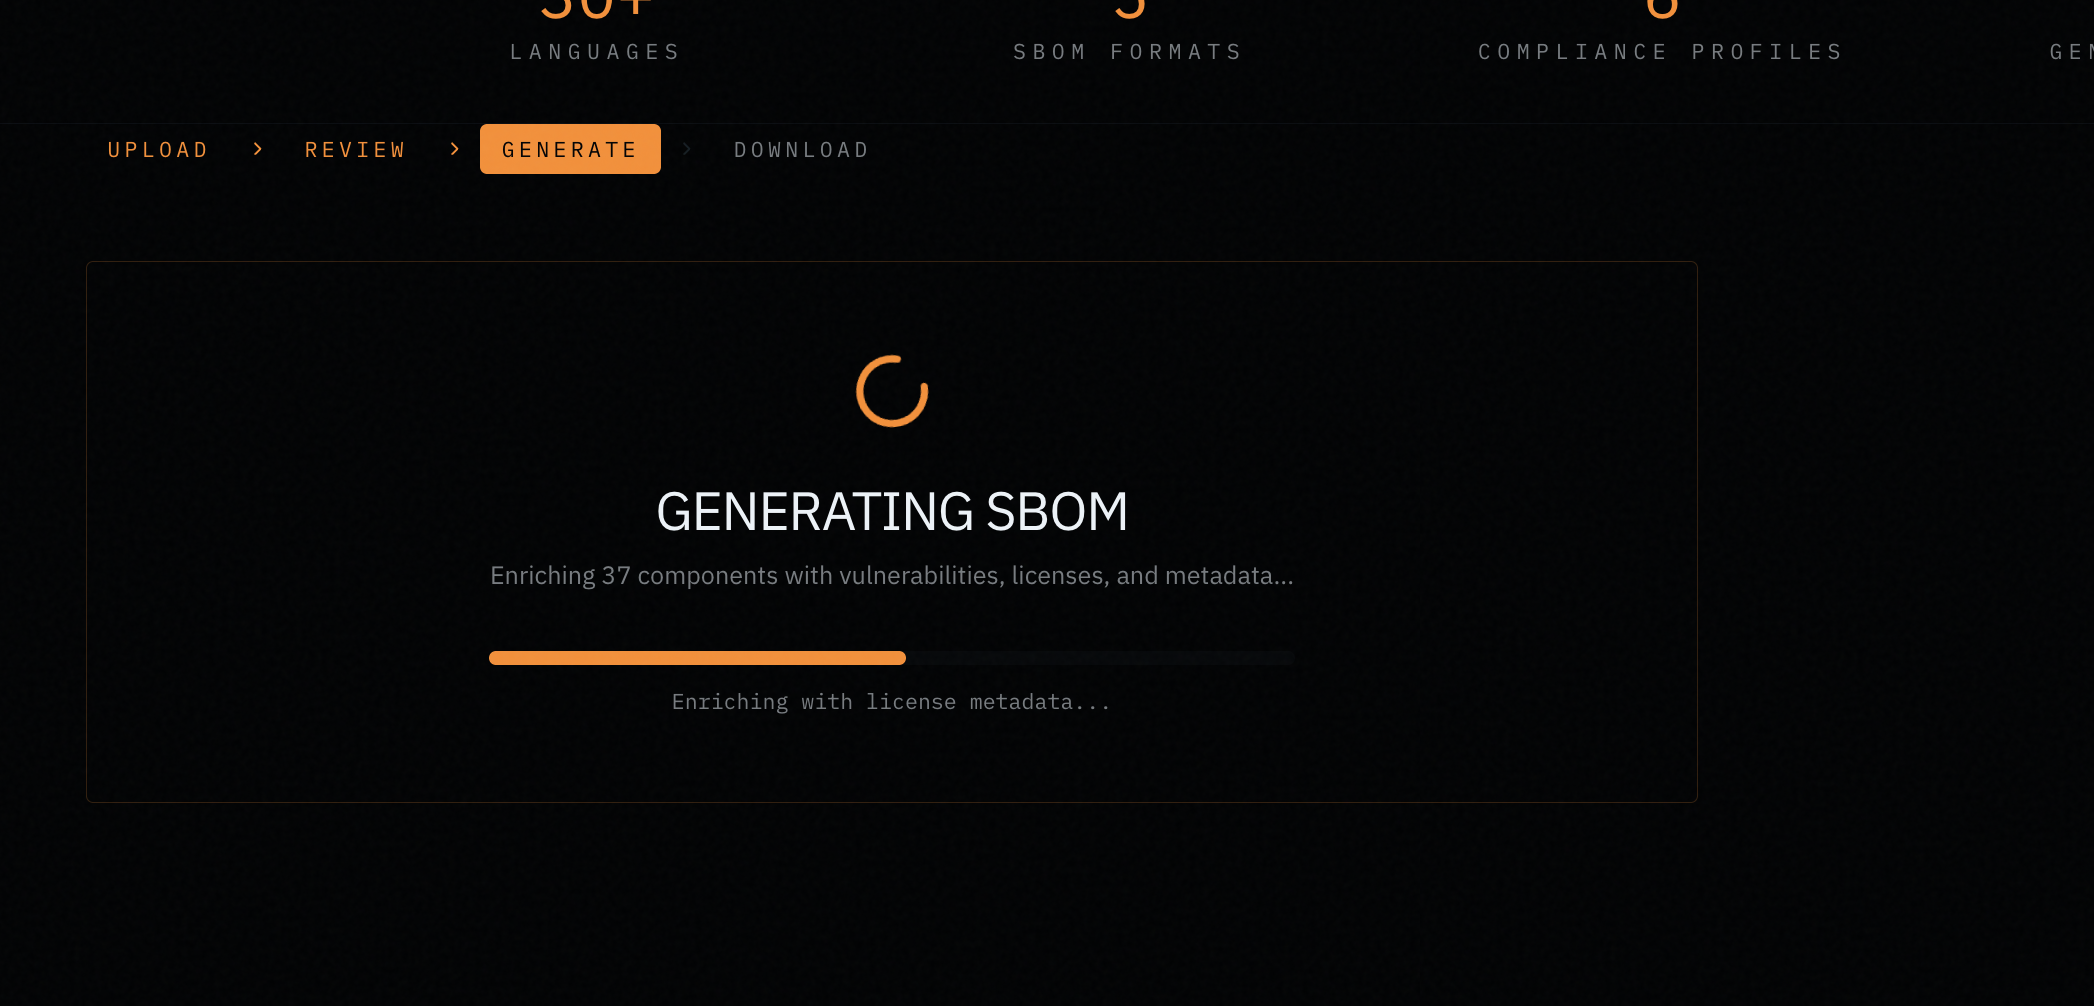
SecureNexus processes your manifest and returns a full CycloneDX 1.6 SBOM enriched with:
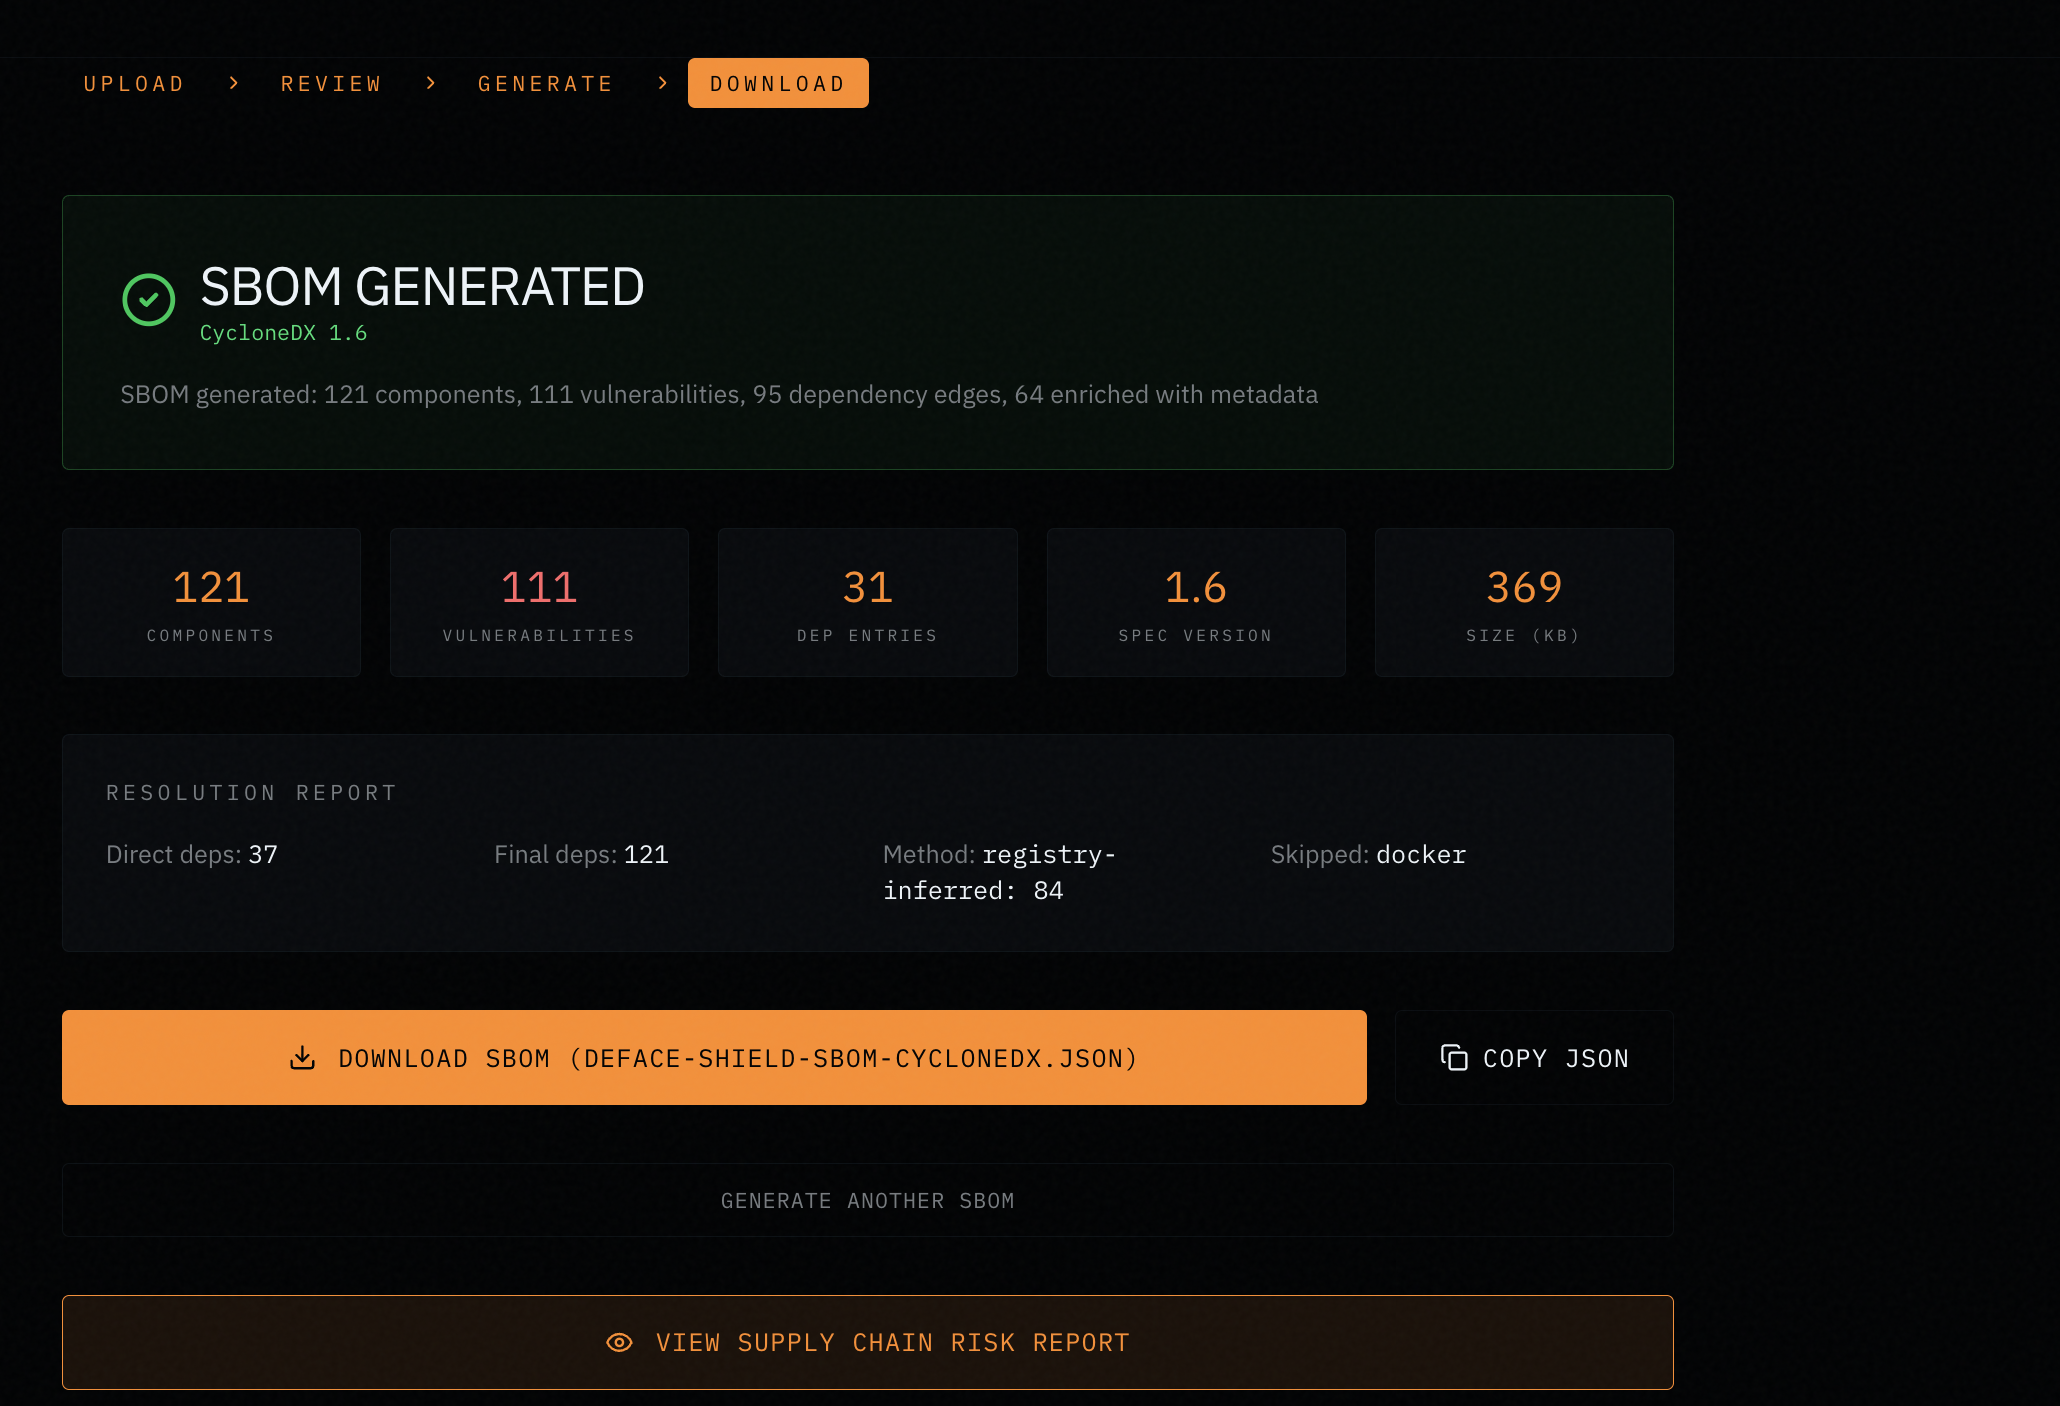
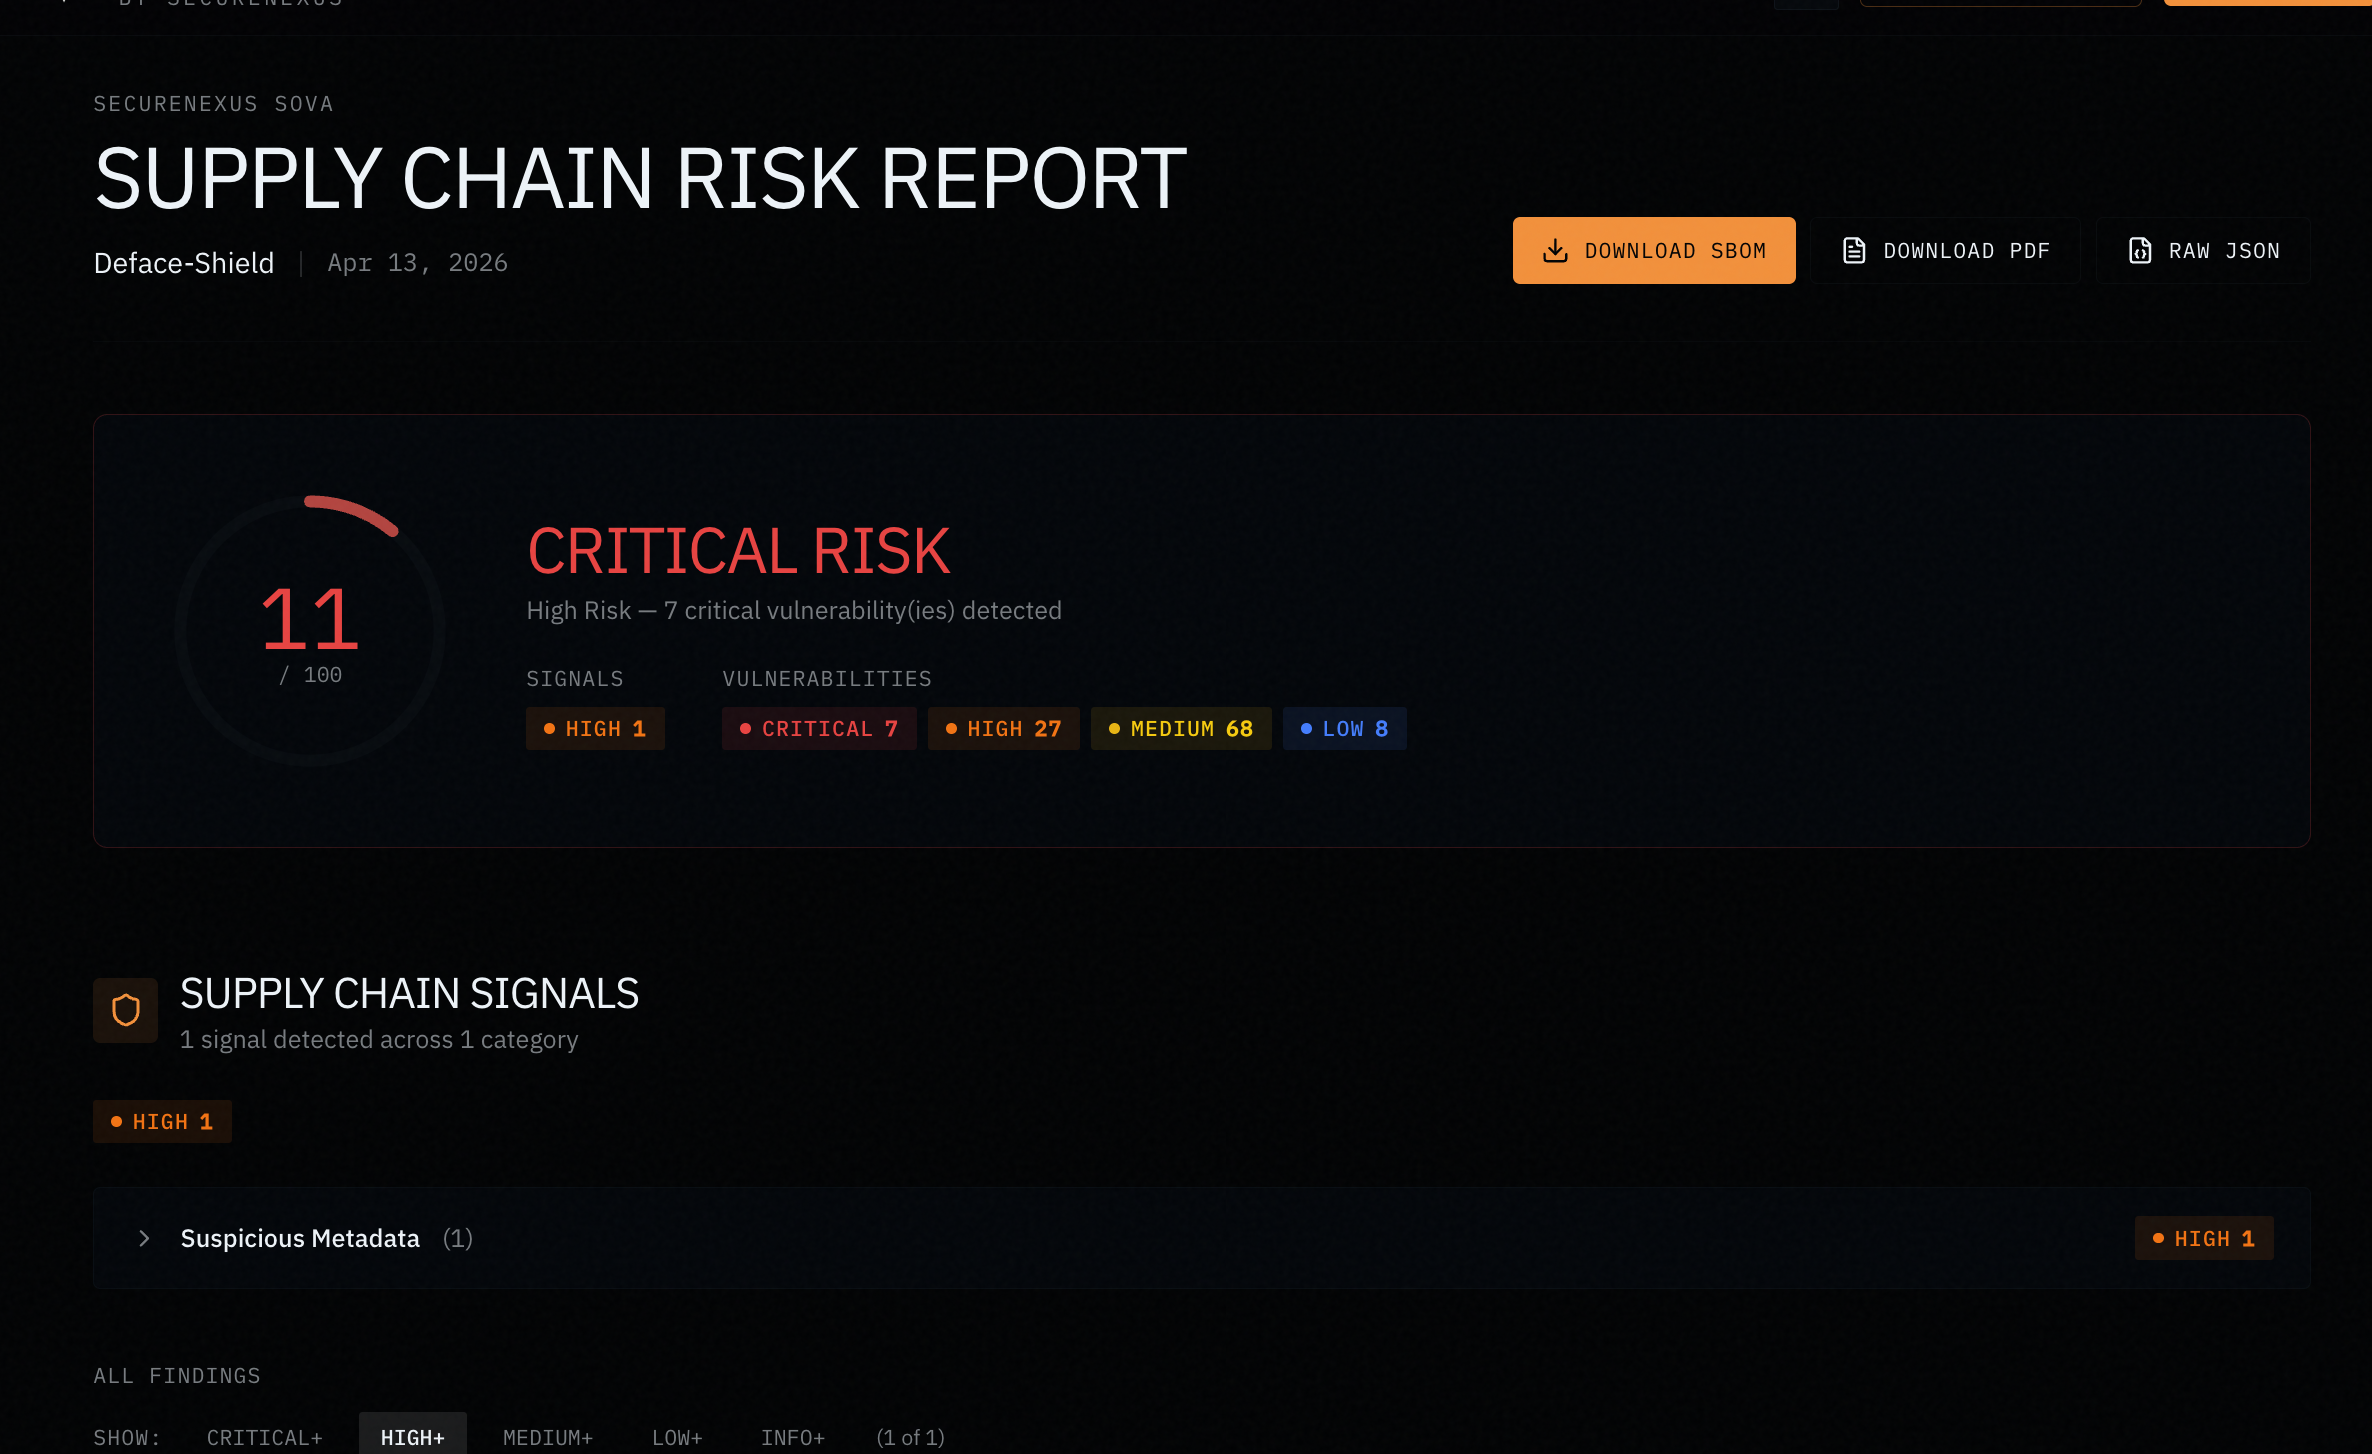
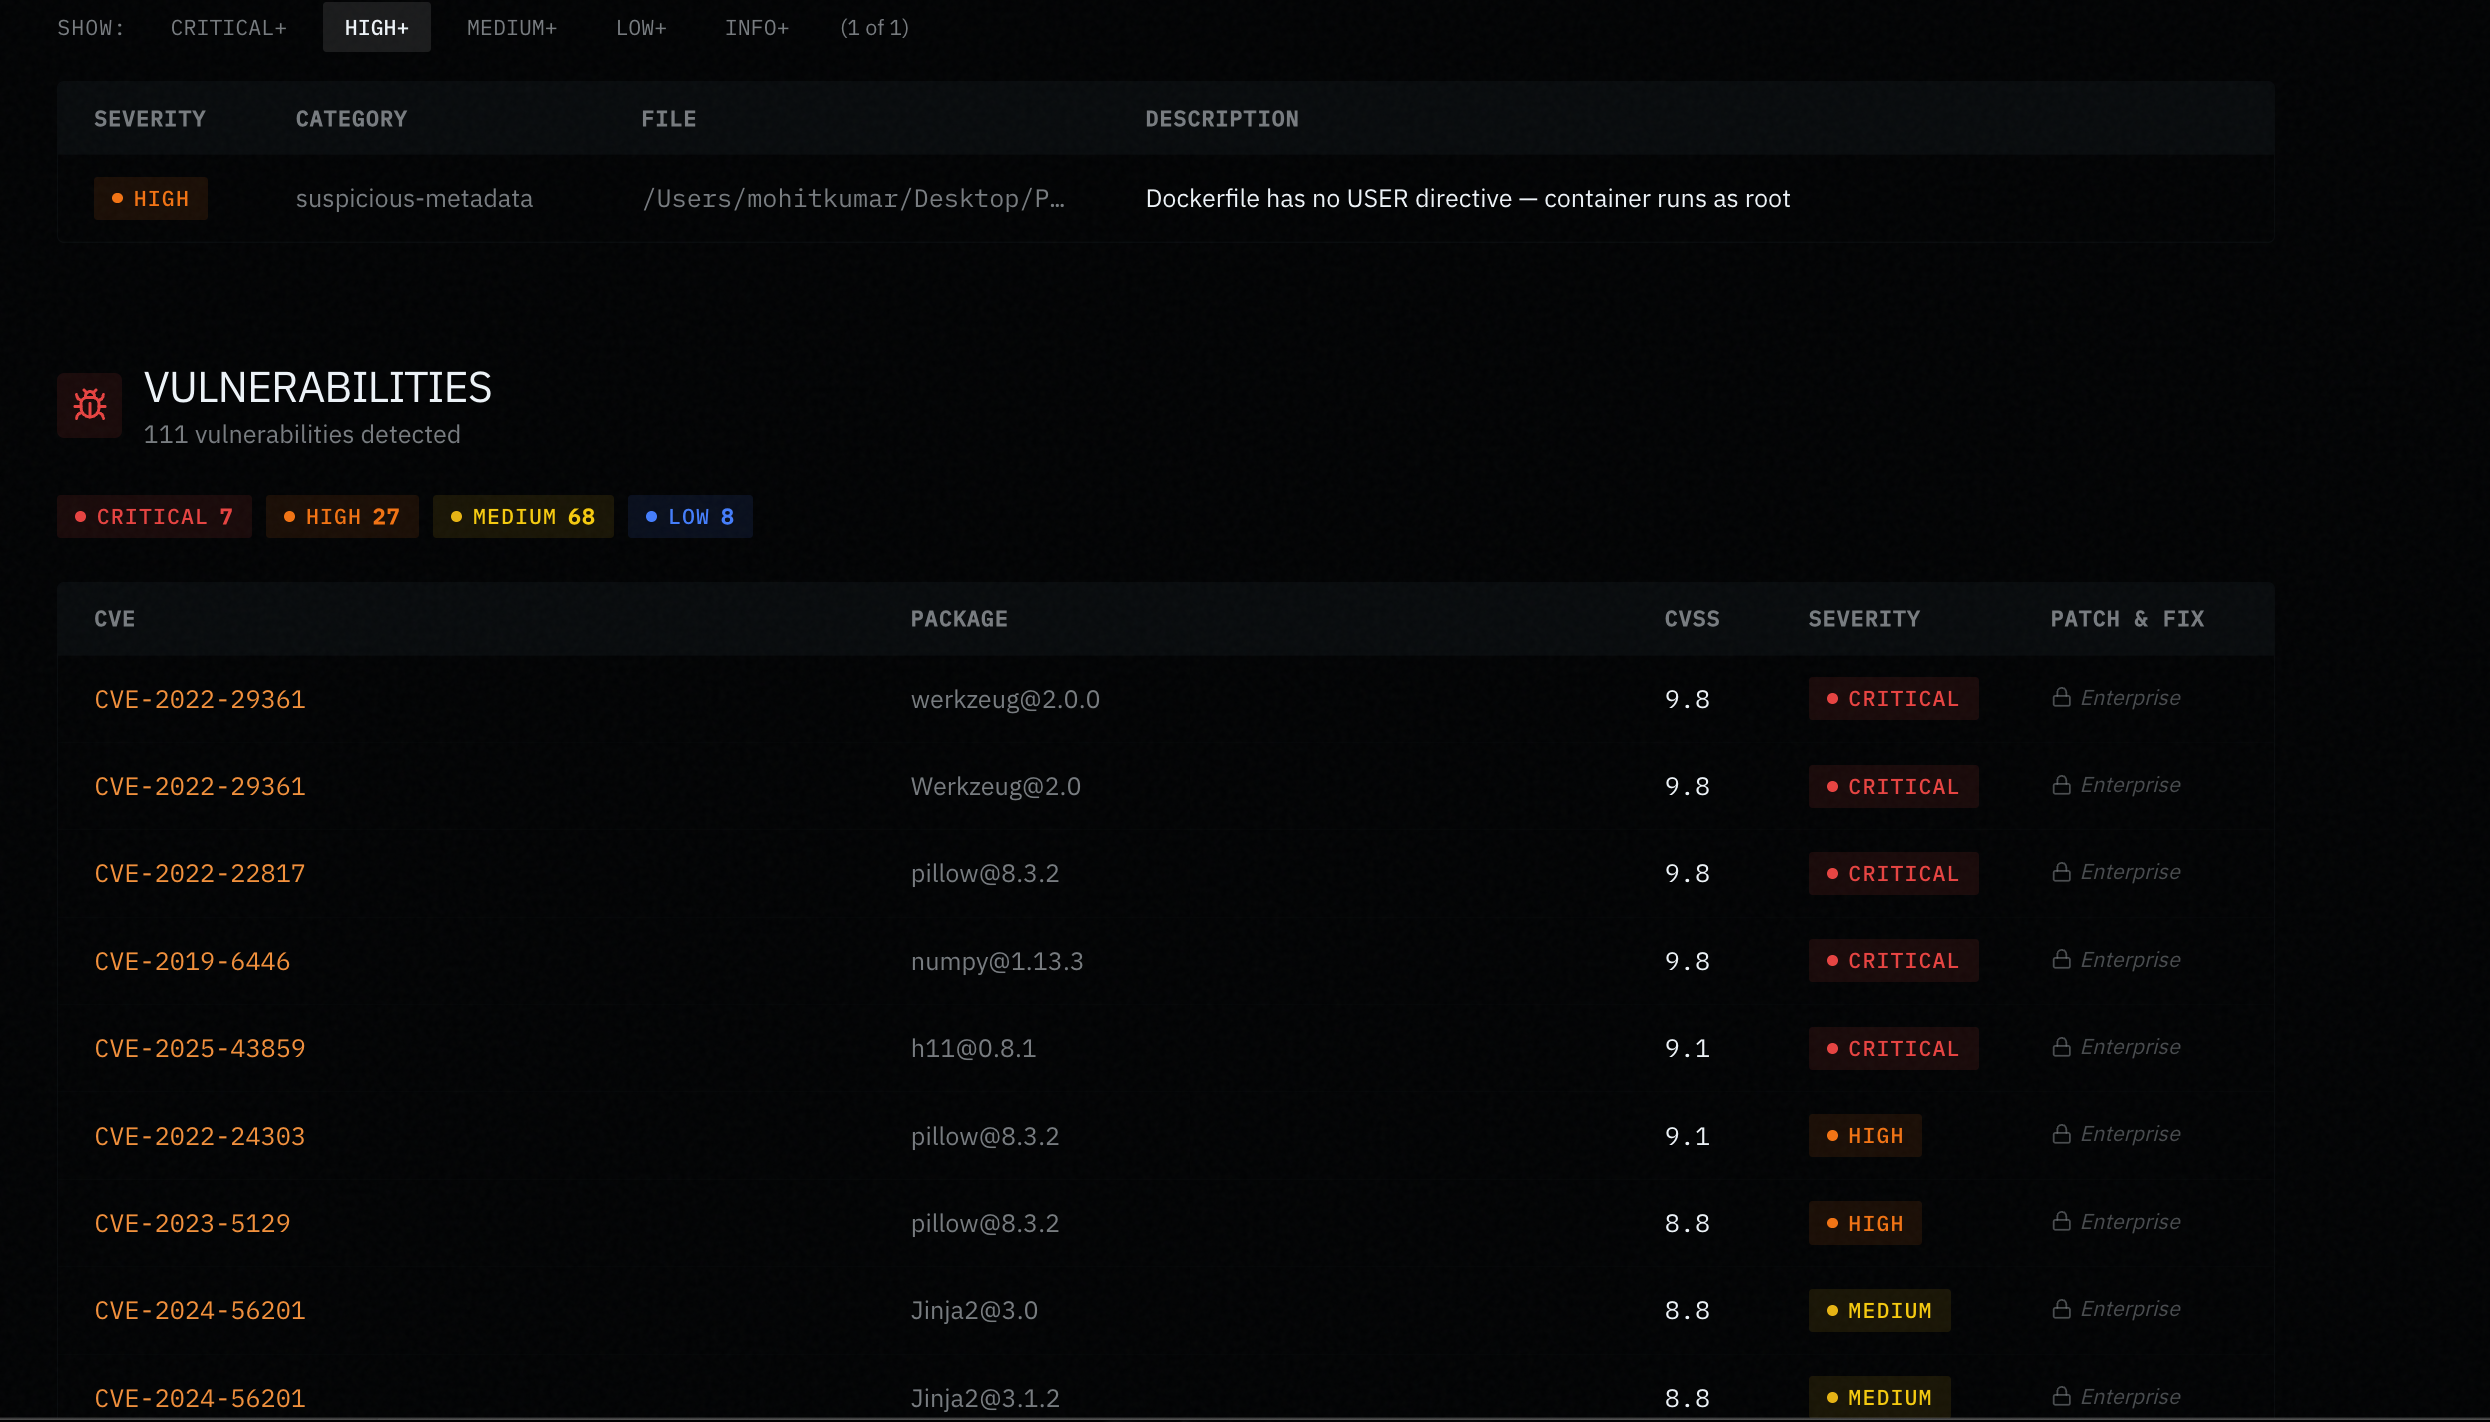
Along with the SBOM, SecureNexus returns a resolution report showing how dependencies were resolved:
{
  "total_direct": 12,
  "total_final": 313,
  "languages_resolved": ["javascript", "python", "rust"],
  "languages_skipped": [],
  "method_breakdown": {
    "registry_lookup": 289,
    "lock_file_graph": 24
  }
}Automate SBOM generation in your pipeline. Run SOVA in CI, upload the manifest, and gate releases on vulnerability findings.
name: SBOM Generation
on: [push]

jobs:
  sbom:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v4

      - uses: actions/setup-node@v4
        with:
          node-version: '20'

      - name: Install SOVA
        run: npm install -g @securenexus/sova

      - name: Scan project
        run: sova scan --path . --strip-paths --quiet --output sova-manifest.json

      - name: Upload manifest artifact
        uses: actions/upload-artifact@v4
        with:
          name: sova-manifest
          path: sova-manifest.json
Tip: Use --quiet in CI to suppress the banner and --strip-paths to avoid leaking runner directory paths in the manifest.
If SOVA detected any supply chain security signals during the scan, they are included in the manifest and carried through to the SBOM. The SecureNexus report displays them alongside CVE vulnerabilities for a complete risk picture.
"securitySignals": {
  "totalSignals": 3,
  "critical": 1,
  "high": 2,
  "medium": 0,
  "low": 0,
  "signals": [
    {
      "file": "package.json",
      "language": "javascript",
      "category": "install-script",
      "type": "npm-postinstall-script",
      "description": "postinstall script executes shell command",
      "severity": "critical"
    },
    ...
  ]
}
See Signal Categories for the full list of 10 detection categories and Threat Model for severity guidance.
Upload your sova-manifest.json and generate a full CycloneDX SBOM in seconds.